Protect Your Website With Cloudflare
If your website is receiving bot attacks, scraping, brute-force attempts, spam traffic, abusive requests, or unwanted traffic that increases server load, I can review and improve your Cloudflare security configuration.
I configure protection based on your website, traffic patterns, and the features available on your current Cloudflare plan. The goal is to reduce malicious and unnecessary traffic while keeping legitimate visitors, search engines, APIs, and important website functions working normally.
What I Can Configure
- Cloudflare WAF custom rules
- Bot and crawler filtering
- Rate limiting
- WordPress login protection
- wp-admin and wp-login.php protection
- Country and IP filtering where appropriate
- Brute-force attack mitigation
- Scraping and abusive traffic protection
- Security Events review
- DNS and proxy configuration review
- SSL/TLS settings review
- Cloudflare caching and performance settings
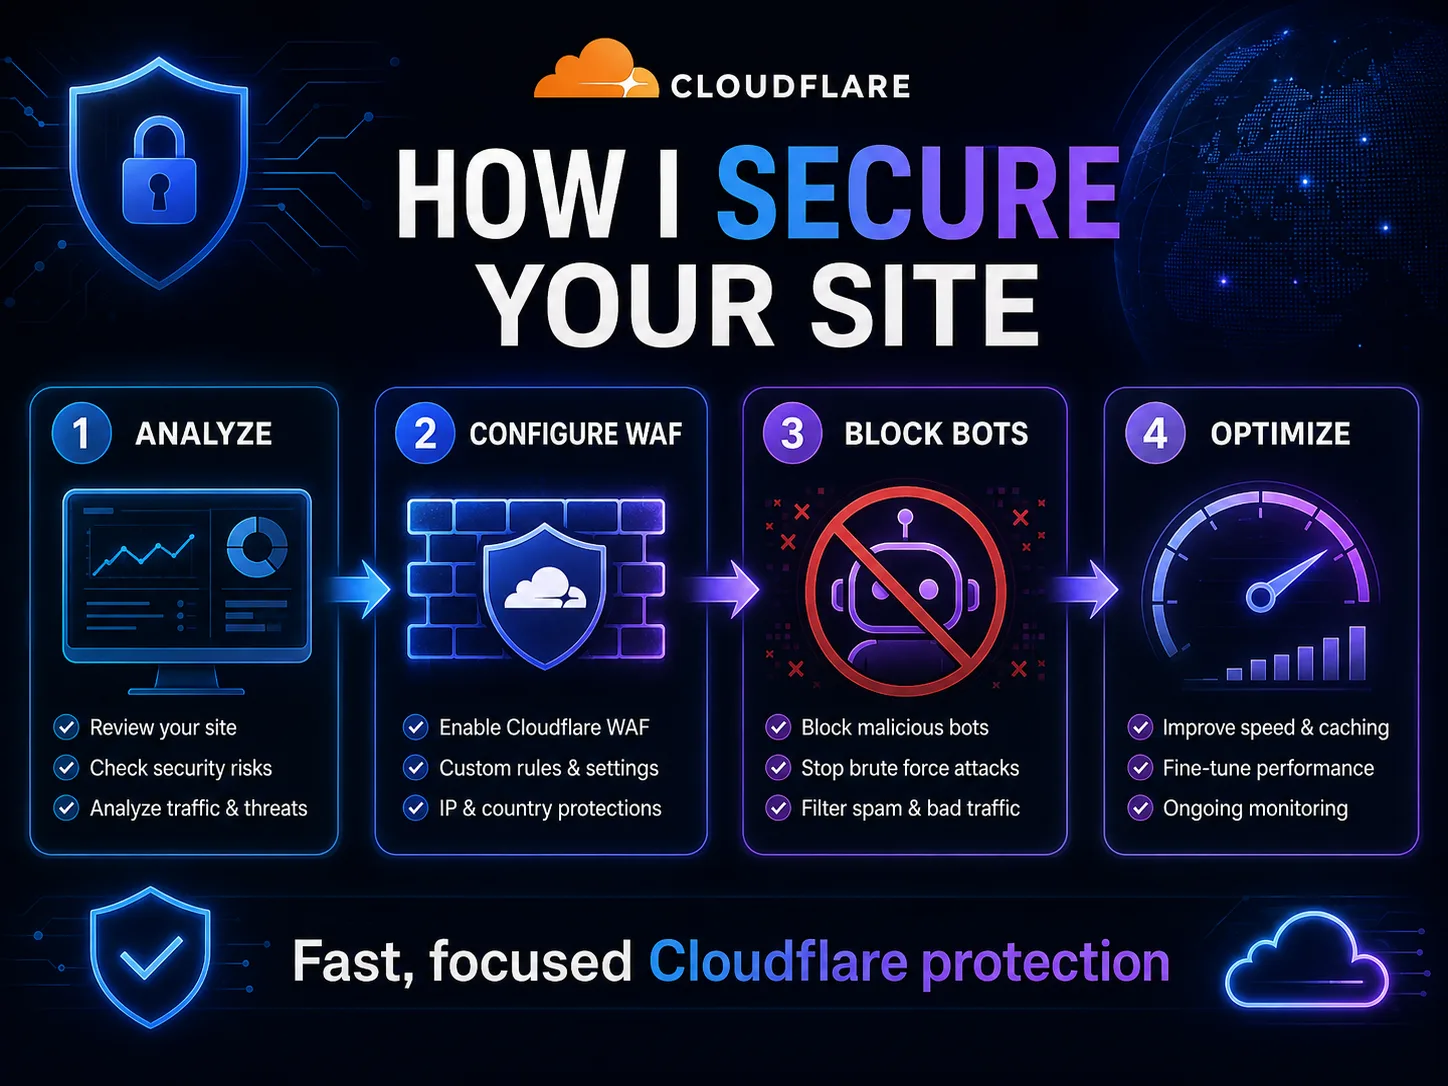
How I Work
1. Security & Traffic Analysis
I review your existing Cloudflare configuration, Security Events, traffic patterns, website platform, and available hosting or server information to identify threats, unnecessary traffic, and weak points.
2. WAF & Bot Protection Setup
I configure suitable WAF rules, rate limiting, login protection, bot controls, IP or country filtering, and other relevant security settings based on your website and Cloudflare plan.
3. Testing & Optimization
I review legitimate traffic behavior and test the protection to reduce the risk of blocking real users, search engines, APIs, payment systems, or other important website services.
4. Final Verification
I verify the final configuration and review the main security and performance changes made to your Cloudflare setup.
WordPress & WooCommerce Protection
For WordPress websites, I can pay particular attention to commonly abused endpoints such as:
- wp-login.php
- wp-admin
- xmlrpc.php
- WordPress REST API routes
- admin-ajax.php
- Search and dynamic URLs
- WooCommerce and other important application endpoints
Rules are designed around the website's actual functionality instead of blindly blocking WordPress endpoints that may be required by plugins or legitimate users.
Cloudflare Performance Review
Blocking unnecessary requests before they reach your hosting server can reduce server load in many situations. I can also review relevant Cloudflare caching, compression, proxy, and performance settings where appropriate.
Actual performance improvements depend on the website, hosting environment, application, plugins, traffic, and existing configuration.
Cloudflare Plan Requirements
Cloudflare Free includes useful security features, but some advanced WAF, bot-management, rate-limiting, and other capabilities may depend on your Cloudflare plan.
I will use the features available on your current plan and recommend an upgrade only when a required feature genuinely needs it.
Important
No firewall configuration can guarantee that every attack will be stopped or that zero false positives will occur. I design and test rules carefully to minimize disruption to legitimate traffic while improving practical protection.
If your website is currently under a severe attack, experiencing major downtime, or requires Cloudflare Enterprise-only functionality, contact me first so I can review the situation.
Need Better Cloudflare Protection?
Send me your website URL and briefly describe the problem, such as bot traffic, scraping, brute-force attacks, high server load, suspicious traffic, or repeated security events.